Thursday, March 07, 2019

Should be amusing. Will the government reveal specifics or rely on the “it could happen” argument?
Huawei Takes US to Court over Ban, Cyberespionage Accusations
… Huawei decided to take the US government to court not only because of the restriction of business in the US, but also the accusations that it poses a threat to national security and the call for other countries to ban its 5G technology, the telecom said on Thursday, according to The Guardian.
The lawsuit, filed in federal court in Texas, hinges on a legislative act that prohibits as unconstitutional the act of depriving a group of a trial and declaring the party guilty.
… “The US Congress has repeatedly failed to produce any evidence to support its restrictions on Huawei products. We are compelled to take this legal action as a proper and last resort.”


A clear area where AI could improve security? All it would need to do is identify employees who have no connection to patient treatment. (Not as easy as it sounds.)
Dana Kozlov reports:
Dozens of workers at Northwestern Hospital may have been fired for improperly reviewing the medical records of Jussie Smollett, who was treated at the emergency room after he claimed he had been attacked by two men.
Sources say those workers have been terminated after gaining access to the “Empire” actor’s medical chart. Smollett has since been charged with staging the whole incident.
Read more on CBS.


Part of this strategy seems to be a recognition that GDPR like laws will proliferate.
Mark Zuckerberg says his vision to divide Facebook's products in 2 could put its $56 billion business model at risk
… Facebook has been signalling a pivot to privacy for months, but on Wednesday, CEO Mark Zuckerberg slammed the reset button in a thoughtful blueprint for the future.
In essence, Zuckerberg sets out a plan to split the Facebook product in two. To use his analogies, he wants to create:
  • A town square, where people can talk to many people at once. Think the Facebook Newsfeed, groups, Instagram posts, and Stories.
  • And a living room— a closed-off space where people can interact privately, using messaging with end-to-end encryption. Think WhatsApp, Messenger, and Instagram DMs.
… But it will come at a cost. End-to-end encryption — along with other plans to give people more control over their data such as a clear history tool and disappearing posts — will make it harder for Facebook to gather the user information on which its business model relies. The company made $55.8 billion in revenue in 2018, the bulk of which came from advertising.


(Related) Another reason to change?
U.S. users are leaving Facebook by the millions, Edison Research says
All the bad press about Facebook might be catching up to the company. New numbers from Edison Research show an an estimated 15 million fewer users in the United States compared to 2017. The biggest drop is in the very desirable 12- to 34-year-old group. Marketplace Tech got a first look at Edison's latest social media research. It revealed almost 80 percent of people in the U.S. are posting, tweeting or snapping, but fewer are going to Facebook.


(Related)
Mark Zuckerberg Tried Hard To Get Facebook Into China. Now The Company May Be Backing Away
“As we build our infrastructure around the world, we've chosen not to build data centers in countries that have a track record of violating human rights like privacy or freedom of expression,” Zuckerberg wrote on Wednesday.


AI impersonating a restaurant customer? What could possibly go wrong?
Google brings its Duplex AI restaurant booking assistant to 43 states
No moment wowed the audience at last year’s I/O more than Duplex. The demo of the artificial intelligence restaurant and appointment booking program left many in the audience wondering whether Google had just pulled a fast one over on them.
Turns out, it’s real.
… Starting this week, Pixel 3 owners in 43 U.S. states will be able to use the Duplex technology to book appointments. The tech should work with any restaurants ... that accept reservations but do not have an online system to complete the booking.
In the coming weeks, the service will be rolled out to users on other Android and iOS devices, as the company continues to tweak the program based on user feedback.


The future? Hacking a fake license will become as easy as it was back when I was an 18, 21 and 24 year old in high school.
Google is working on securely storing Digital Driver's Licenses in Android
Carrying a wallet has become less of a necessity for me since I started using Google Pay to manage my credit cards, but there’s still no way I can travel anywhere without my driver’s license. I know a few people who use wallet cases to hold what few cards they must carry on their person, but I’m waiting for the day when I can legally drive to Walmart with just my phone on me. A digital driver’s license offers multiple advantages over the traditional ID card. You can’t lose it, you can update it remotely so you don’t have to stand in line at the DMV, you can wipe it remotely if your phone gets stolen, you’re less likely to get your identity stolen since you don’t need to carry a wallet with easily accessible information, you’re less likely to leave your phone at home, and you’ll have an easier time bringing it up on request. Authorities across the U.S. are slowly recognizing the benefits of a mobile driver’s license, which is why we’re hearing more U.S. states test their adoption each year.
… digital security company Gemalto is partnering with Colorado, Idaho, Maryland, Washington D.C., and Wyoming to run pilot programs before rolling out their digital driver’s license solution. At the same time, the American Association of Motor Vehicle Administrators is working to standardize this new form of electronic identification.


Should interest our programming students.
Microsoft open-sources its Windows calculator on GitHub
Microsoft is making the source code for its Windows calculator available on GitHub today. The software maker wants to “build an even better user experience in partnership with the community.” Opening up the calculator means anyone can contribute code to improve the app
… The source code is now available on GitHub and it includes the build system, unit tests, and even the product road map for the calculator feature in Windows.


Wednesday, March 06, 2019

My students can not understand why I don’t own a smartphone. This may be part of the reason: Without one, I don’t exist.
Phone numbers are the new Social Security numbers
Axios: “Cellphone numbers have become a primary way for tech companies like Facebook to uniquely identify users and secure accounts, in some ways becoming a proxy for a national ID.
Why it matters: That over-reliance on cellphone numbers ironically makes them a less effective and secure authentication method. And the more valuable the phone number becomes as an identifier, the less willing people will be to share it for communication.
Driving the news: Facebook faced criticism this week for its handling of phone numbers that users provide for the purpose of two-factor authentication (2FA) — in which a person’s login is protected by both a password and a device like their smartphone.
The big picture: American culture and law are hostile to establishing any sort of national ID, leaving businesses and organizations to find substitute… Many Americans try to avoid broadcasting SSNs online. But now people have to share them with so many institutions and clerks that there’s very little that’s truly secret about them…”


For my Computer Forensics and Ethical Hacking students. Just a couple small tweaks and this becomes quite useful!
NSA Makes Reverse Engineering Tool Freely Available
Initially announced in January, the release was accompanied by a demonstration of the tool at the RSA Conference 2019, which is taking place this week in San Francisco.
Ghidra, the NSA explains, is a software reverse engineering (SRE) suite of tools developed by the agency’s Research Directorate to analyze malicious code and malware, as well as to provide cyber-security researchers with information on potential vulnerabilities in their networks and systems.
The framework packs various software analysis tools compatible with multiple platforms, including Windows, macOS, and Linux, and provides capabilities such as disassembly, assembly, decompilation, graphing and scripting, and more.


Redefining ‘Jurisdiction’ for the Internet Age?
BREAKING: United States Supports Germany’s International Arrest Warrant for Accused Syrian War Criminal
On Tuesday, the United States government issued a statement supporting Germany’s request to Lebanon to extradite a high-ranking Syrian official accused of war crimes and crimes against humanity. Former officials from the Obama and Trump administrations spoke to me about the significance of this development.
By taking this step, the United States placed itself on the record in support of Germany’s exercise of a form of “universal jurisdiction,” a move that marks a significant development in U.S. legal practice. Under section 1 of the 2002 Code of Crimes Against International Law, German courts are allowed to exercise criminal jurisdiction over an accused person who has committed war crimes, crimes against humanity, or genocide—regardless of where the crimes were committed, regardless of whether the accused has any connection to Germany, and regardless of the nationality of the victims at the time the crimes were committed.


I found an amusing new term!
Amy Webb’s ‘The Big Nine’ predicts the impact of AI and tech giants over the next 50 years
… “We stop assuming that the G-MAFIA (Google, Microsoft, Apple, Facebook, IBM, and Amazon) can serve its DC and Wall Street masters equally and that the free markets and our entrepreneurial spirit will produce the best possible outcomes for AI and humanity,” author Amy Webb writes.


Minutes keep getting busier.
2019: This Is What Happens In An Internet Minute


For my Excel toolkit.


I do like lists, but “most widely available” is not the same as “best.”
OCLC publishes list of top 100 novels
“OCLC, a leading library technology and research organization, has published The Library 100: Top Novels of All Time, a list of the novels most widely available in libraries today. The list is based on data in WorldCat, the world’s most comprehensive database of information about library collections. Produced and maintained by OCLC and individual member libraries and library organizations, WorldCat reflects the collections of more than 18,000 libraries worldwide. It includes information about more than 2.7 billion copies of more than 447 million titles. This aggregate worldwide library collection is likely the best view of the global scholarly and published record.
  • The full list, and more information about The Library 100 can be found at https://www.oclc.org/en/worldcat/library100.html.
  • …”Of course, the list of top novels emphasizes classics,” Prichard continued, “and so reflects dominant cultural views over the years about the canon and its formation. Librarians are aware of this and are more mindful than ever of the need to think critically about their collections. Librarians are actively seeking out and preserving overlooked, minority and marginalized perspectives.” (Read Prichard’s blog post at https://oc.lc/top-novel-blog.)…


Tuesday, March 05, 2019

I’m guessing they won’t need to do this in the US. We’re much more ambiguity tolerant.
Google to ban political ads ahead of federal election, citing new transparency rules
Google is banning political advertising on its platforms ahead of the Canadian federal election because of new ad transparency rules it says would be too challenging to comply with.
The decision comes in response to the Liberals’ signature election measure, Bill C-76, which passed in December. Among other things, it requires online platforms to keep a registry of all political and partisan ads they directly or indirectly publish.
… Aside from the ad registry requirement, Google also expressed concerns about how it would detect ads of a partisan nature, which may not specifically mention a candidate or party by name. “The challenge for us is that that definition is extremely broad,” Mr. McKay said.


If true, why is it being announced by an aide? No one wants to take credit?
Disputed N.S.A. Phone Program Is Shut Down, Aide Says
The National Security Agency has quietly shut down a system that analyzes logs of Americans’ domestic calls and texts, according to a senior Republican congressional aide, halting a program that has touched off disputes about privacy and the rule of law since the Sept. 11 attacks.
The agency has not used the system in months, and the Trump administration might not ask Congress to renew its legal authority, which is set to expire at the end of the year, according to the aide, Luke Murry, the House minority leader’s national security adviser.


Perhaps individual opinions are not universal?
EU ‘Terrorist Content’ Proposal Sets Dire Example for Free Speech Online
… Last year, the German parliament enacted the NetzDG law, requiring large social media sites to remove posts that violate certain provisions of the German code, including broad prohibitions on “defamation of religion,” “hate speech,” and “insult.” The removal obligation is triggered not by a court order, but by complaints from users.
… While NetzDG required companies to create mechanisms to lodge complaints about posts, it failed to include parallel requirements for challenging removals. Within hours after it went into effect, warnings that the law would sweep too broadly were vindicated: Twitter deleted tweets from a far-right politician, as well as those of a satirical magazine that made fun of her.


PreCrime!
These Cameras Can Spot Shoplifters Even Before They Steal
… While AI is usually envisioned as a smart personal assistant or self-driving car, it turns out the technology is pretty good at spotting nefarious behavior. Like a scene out of the movie “Minority Report,” algorithms analyze security-camera footage and alert staff about potential thieves via a smartphone app. The goal is prevention; if the target is approached and asked if they need help, there’s a good chance the theft never happens.


More on surveillance.
Chad Marlow of the ACLU has an article that I would encourage parents of school-age children to read.  And if you don’t have school-age kids, but just generally give a damn about letting little kids grow up to become adults instead of getting gunned down at school, read it anyway. Here’s just one snippet:
there is no demonstrated link between increasing student surveillance and decreasing gun violence on campus.
To the contrary, student surveillance — and indeed surveillance in general — has been shown to have no deterrent effect on violent crime. And one should not fall into the false forward-versus-backward analysis trap: Even if, after-the-fact, many school shooters are found to have posted threatening statements online, that doesn’t mean most, or even a significant number of students who post threatening statements are likely to become school shooters.
Do you know what the Dickey and Tiahrt Amendments are and how they are preventing us from getting meaningful research on stemming gun violence in schools? No? A lot of us didn’t/don’t know. But it’s time we all became more educated and insistent on really addressing the problem of gun violence at schools properly and effectively.
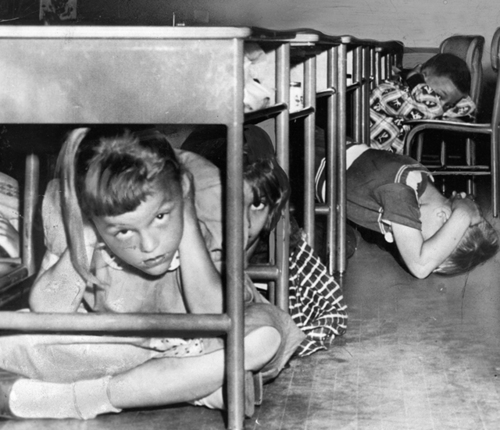
I grew up in the generation where we had atomic bomb drills in school. Today’s kids are growing up with active shooter drills. In one way, I think things are worse now because today’s kids are worrying about a fellow student or former student who comes in, looks them in the eye, and tries to take their life. Not someone remotely pushing a button that drops a bomb on the whole building or town, but someone you may know having the intent and means to kill you or your little brother down the hall….
What are we doing to children?
Read the ACLU’s post and stop drinking the Kool-Aid that the NRA hands out with one hand while providing campaign financing with the other hand.


A noble goal, but I don’t see a clear answer here.
How to Build Artificial Intelligence That Everyone Can Trust
Experts from IBM Watson and Kellogg discuss how to remove bias and increase transparency in machine-learning algorithms.


For my next Disaster Recovery lecture.
For Fukushima's nuclear disaster, robots may be the only hope


Perspective. Find something India wants, set sales records.
Spotify adds 1 million unique listeners in India in less than a week
Spotify Technology SA, the world’s most popular paid music streaming service, said it racked up more than 1 million unique users in India across its free and premium tiers since launching less than a week ago.
Spotify launched in India on Tuesday, stepping into a price-sensitive market crowded by well-funded players such as Reliance Industries’ JioSaavn and Apple’s Apple Music.
The Swedish company is offering a free version that will run with ads, alongside a premium ad-free variant that will charge users 119 Indian rupees ($1.68) per month.


Worth a try?
Shaking the Chrome habit is getting easier – try Brave
The Verge – Vlad Savov: “Readers of this august website may recall that a year ago, I lauded Firefox and its progress toward becoming a genuine alternative to Google’s dominant Chrome browser. As much as I liked where Firefox was going, however, I couldn’t stick with it over the long term. It wasn’t compatible with everything the way Chrome was, its extensions were different, and, for my way of using a browser, it was slower and less responsive. So I returned to Chrome after a few weeks of Firefox, but the urge to decouple my browsing habits from Google remained.


Dive deep!
Free Reading Spree to Kick Off Spring
We’re gearing up to release our Spring 2019 issue, which features an exciting lineup of big ideas from key management thinkers. To celebrate its publication in advance, we’re dropping our paywall on March 5 and 6 so that all of our content will be freely available to visitors online.


Monday, March 04, 2019

If you don’t want to unleash the nukes, what’s the next best thing?
Fossbytes reports:
A recent report by Hindustan Times stated that hackers from Pakistan attacked over 90 websites of the Indian Government. The recent escalations in tensions between the neighbors led to a surge in attacks in cyberspace, targeting key infrastructures.
The death of 40 CRPF personnel in a recent terror strike by Pakistan-based Jaish-e-Mohammad led to India retaliating with airstrikes on terrorist launch pads in Balakot, Pakistan. The attack is said to have wiped out a few hundred terrorists including leader Masood Azhar’s brother in law, Yousuf Azhar.
Read more on Fossbytes.
[From the article:
As reported on the 18th of Feb, Indian hacktivists had retaliated in cyberspace by hacking over 200 websites of the Pakistan Government, some of which are still not accessible from outside Pakistan.


The constant competition of capitalist China.
1 in 5 corporations say China has stolen their IP within the last year
  • Theft of intellectual property by Chinese companies is a major point of contention between the Trump administration and Chinese government.
  • Just under one-third of CFOs of North America-based companies on the CNBC Global CFO Council say Chinese firms have stolen from them at some point during the past decade.
  • U.S. trade policy remains a negative for businesses around the world, but right now European CFOs are expressing the biggest concerns about trade policy as an external risk factor…”


Security backgrounder.
IBM X-Force Intelligence Threat Index 2019
“As the cyber threat landscape evolves, what we saw in 2018 is organisations across all industries are facing unmanageable levels of cyber threats brought on by the changing threat landscape, the risk of exposure and an ever-growing attack surface. The IBM X-Force Research team is a crack team of security professionals who run thousands of spam traps around the world and monitor tens of millions of spam and phishing attacks daily while analysing billions of web pages and images to detect fraudulent activity and brand abuse. In the fight to stay one step ahead, this week we released the IBM X-Force Intelligence Threat Index 2019. The report contains notable security events in 2018 and looks ahead with a pre-emptive approach. It also shares insights and observations from data analysed via hundreds of millions of protected endpoints and servers across over 100 countries…
Some of the key findings in the report include: Ransomware & Malware are out & cryptojacking is in…”


(Related)
Cisco Publishes Annual CISO Benchmark Study
… Cisco's 2019 Chief Information Security Officer (CISO) Benchmark Study has one great strength. It queried more than 3,200 senior leaders with a CISO role (if not title) from 18 different countries.
… The report (PDF) states, "ML, AI and more automation should be able to boost security efforts exponentially – and next year we need to see more respondents in the 'completely reliant' phase of implementation and practice."


Another perspective on AI.
New on LLRX – Nothing Artificial About It: How Law Firms (Really) Use AI in Practice
Via LLRX – Nothing Artificial About It: How Law Firms (Really) Use AI in Practice – Ed Walters, CEO of Fastcase, talks about how the new age of law firm innovation is changing legal services by moving from anecdotal to data-driven insights and thus providing better-informed guidance for clients. Walters also identifies the value of analytics to manage and mitigate risk, which he points out is almost always more cost effective than litigating the effects after the fact. Most importantly, Walters highlights not only how law firms are using AI, but that they are also building their own tools to deliver new types of services as well.


My AI reading list.
What Is The Best Book On Artificial Intelligence (AI)?
… honestly, it was just too difficult to narrow down my favorites to one book!
Instead, I offer you my top five.
The Fourth Age: Smart Robots, Conscious Computers, and the Future of Humanity
Life 3.0: Being Human in the Age of Artificial Intelligence
Homo Deus: A Brief History of Tomorrow By Yuval Noah Harari
AI Superpowers: China, Silicon Valley And The New World Order
Human + Machine: Reimagining Work in the Age of AI


Not exactly household names… How did GDPR change their practices?
Here are the data brokers quietly buying and selling your personal information
FastCompany: “It’s no secret that your personal data is routinely bought and sold by dozens, possibly hundreds, of companies. What’s less known is who those companies are, and what exactly they do. Thanks to a new Vermont law requiring companies that buy and sell third-party personal data to register with the Secretary of State, we’ve been able to assemble a list of 121 data brokers operating in the U.S. It’s a rare, rough glimpse into a bustling economy that operates largely in the shadows, and often with few rules. Even Vermont’s first-of-its-kind law, which went into effect last month, doesn’t require data brokers to disclose who’s in their databases, what data they collect, or who buys it. Nor does it require brokers to give consumers access to their own data or opt out of data collection. Brokers are, however required to provide some information about their opt-out systems under the law–assuming they provide one. If you do want to keep your data out of the hands of these companies, you’ll often have to contact them one by one through whatever opt-out systems they provide… Those include big names in people search, like Spokeo, ZoomInfo, White Pages, PeopleSmart, Intelius, and PeopleFinders; credit reporting, like Equifax, Experian, and TransUnion; and advertising and marketing, like Acxiom, Oracle, LexisNexis, Innovis, and KBM…”


Well, this didn’t take long. Apparently someone listened to his announcement.
How John Hickenlooper Could Win The 2020 Democratic Nomination


Sunday, March 03, 2019

The Privacy Foundation (https://www.law.du.edu/privacy-foundation) has stirred up some real interest or at least some concerns with our April 19th (changed from the 26th) seminar on “Current California Privacy Legislation” We’re even getting articles submitted that discuss (attempt to explain?) the law. Here are a few:


A quick comparison of California and GDPR
https://www.pwc.com/us/en/services/consulting/cybersecurity/california-consumer-privacy-act.html
Your readiness roadmap for the California Consumer Privacy Act (CCPA)


(Registration required)
https://www.law.com/corpcounsel/2018/12/10/a-practical-guide-to-ccpa-readiness-implementing-calif-s-new-privacy-law-part-1/
A Practical Guide to CCPA Readiness: Implementing Calif.’s New Privacy Law (Part 1)

CCPA is an unfamiliar type of law for the United States due, in large part, to its broad scope. It establishes a new privacy framework for businesses that fall within its jurisdiction.

… the most far-reaching privacy law in the United States.


A comparison PDF
https://fpf.org/wp-content/uploads/2018/11/GDPR_CCPA_Comparison-Guide.pdf


A comparison chart (PDF)
https://www.bakerlaw.com/webfiles/Privacy/2018/Articles/CCPA-GDPR-Chart.pdf


Should Facebook ignore legislation it thinks will have a negative impact on the company? We’re talking degree here, not direction.
https://www.theguardian.com/technology/2019/mar/02/facebook-global-lobbying-campaign-against-data-privacy-laws-investment
Revealed: Facebook’s global lobbying against data privacy laws
Facebook has targeted politicians around the world – including the former UK chancellor, George Osborne – promising investments and incentives while seeking to pressure them into lobbying on Facebook’s behalf against data privacy legislation, an explosive new leak of internal Facebook documents has revealed.
The documents, which have been seen by the Observer and Computer Weekly, reveal a secretive global lobbying operation targeting hundreds of legislators and regulators in an attempt to procure influence across the world, including in the UK, US, Canada, India, Vietnam, Argentina, Brazil, Malaysia and all 28 states of the EU. The documents include details of how Facebook:
• Lobbied politicians across Europe in a strategic operation to head off “overly restrictive” GDPR legislation. They include extraordinary claims that the Irish prime minister said his country could exercise significant influence as president of the EU, promoting Facebook’s interests even though technically it was supposed to remain neutral.
• Used chief operating officer Sheryl Sandberg’s feminist memoir Lean In to “bond” with female European commissioners it viewed as hostile.
• Threatened to withhold investment from countries unless they supported or passed Facebook-friendly laws.


Perspective. Could these be profitable? Implications for self-driving cars?
Shared scooters don't last long
I took a look at data on scooter rides in Louisville, Kentucky, shared online as part of the city’s open data policy. The latest data is available here. The data set I used was older and included monthly data on scooter trips from August through December. It also included a unique “ID” for each scooter, a detail that was key to my analysis and has been stripped out of subsequent data sets published by Louisville. The data doesn’t differentiate between Bird and Lime, but as Bird started operations in August 2018 and Lime that November, you can assume it skews toward Bird.
With that preamble, here are some things I found:
  • The average lifespan of a scooter in Louisville from August to December was 28 days
  • Median lifespan was 23 days
  • If you stripped out scooter IDs that first appeared in December, to focus on older vehicles, the average lifespan increased slightly to 32 days and the median lifespan to 28 days
  • Still stripping out scooter IDs that started in December, the median scooter took 70 trips over 85 miles


Saturday, March 02, 2019

Could social media talk a country into war?
While Two Nuclear Powers Were On The Brink Of War, A Full-Blown Online Misinformation Battle Was Underway
India and Pakistan, both countries that possess over a hundred nuclear warheads each, came close to the brink of war this week. But even as fighter aircraft from both nations invaded each other’s air space, a full-blown misinformation war about the conflict raged on the internet.
“Misinformation has been used to start wars throughout history. It would be foolish to think that our time is the exception to the rule,” Aviv Ovadya, cofounder of the Thoughtful Technology Project, a San Francisco–based nonprofit dedicated to preventing harmful misinformation, told BuzzFeed News.
… India and Pakistan have fought wars previously and have been engaged in a decadeslong territorial dispute over the Kashmir Valley. But this conflict is the first one to take place since social media became ubiquitous.
Fact-checkers in India say that the deluge of misinformation around tensions between India and Pakistan that has flooded the internet is “unprecedented.” Also unusual was the fact that official handles run by the Pakistan army shared two videos (one was later deleted) of the Indian pilot captured on Pakistani soil. The deleted video showed the pilot injured and being escorted away from mobs by Pakistan’s army soon after his plane crashed — it was released before the Indian government confirmed that the pilot was now a prisoner of war, and is still being shared by right-wing Indian WhatsApp groups. The second video, which was shared by the Pakistan military’s official spokesperson soon after, had a palliative effect on revenge-thirsty Indian Twitter: After seeing the Indian pilot praising Pakistani officers for being “thorough gentlemen” and drinking their tea, people online slowly began to favor the hashtag #SayNoToWar, as opposed to #SayYesToWar, which had been trending before.


One definition of “vulnerable.”
America’s Cities Are Running on Software From the ’80s
The only place in San Francisco still pricing real estate like it’s the 1980s is the city assessor’s office. Its property tax system dates back to the dawn of the floppy disk. City employees appraising the market work with software that runs on a dead programming language and can’t be used with a mouse. Assessors are prone to make mistakes when using the vintage software because it can’t display all the basic information for a given property on one screen. The staffers have to open and exit several menus to input stuff as simple as addresses. To put it mildly, the setup “doesn’t reflect business needs now,” says the city’s assessor, Carmen Chu.


Privacy (in the abstract) is bipartisan, nothing else is.
James Strawbridge of Covington & Burling writes:
At a February 27, 2019 hearing on “Privacy Principles for a Federal Data Privacy Framework in the United States,” Republican and Democratic members of the Senate Commerce, Science, & Transportation Committee offered different perspectives on whether new federal privacy legislation should preempt state privacy laws.
Chairman Roger Wicker (R-MS), who described the hearing as a chance to “set the stage” for bipartisan legislation, stressed the importance of preemption, as did Sen. Marsha Blackburn (R-TN). Wicker noted that a national standard would provide greater certainty for consumers, and that a preemptive framework does not necessarily mean “weaker” protections than those included in state privacy laws. Ranking Member Maria Cantwell (D-WA), by contrast, said the focus on preemption (rather than new rights for consumers) was “disturbing,” and wondered if U.S. companies were trying to “shut down” the California Consumer Privacy Act (“CCPA”). Similarly, Sen. Richard Blumenthal (D-CT) warned that U.S. companies must convince Congress that they want “something more” than just preemption.
Despite their apparent differences on preemption, committee members broadly agreed that the “notice and choice” approach to privacy protections is insufficient.
Read more on InsidePrivacy.


For the tool kit.
Microsoft Excel will now let you snap a picture of a spreadsheet and import it
Microsoft is adding a very useful feature to its Excel mobile apps for iOS and Android. It allows Excel users to take a photo of a printed data table and convert it into a fully editable table in the app. This feature is rolling out initially in the Android Excel app, before making its way to iOS soon. Microsoft is using artificial intelligence to implement this feature, with image recognition so that Excel users don’t have to manually input hardcopy data. The feature will be available to Microsoft 365 users.


Friday, March 01, 2019

Noted for future (next year) US elections.
ENISA issues recommendations to protect EU Parliament elections against cyber-threats
… To combat foreign interference such as that witnessed in the US presidential elections in 2016, ENISA is providing guidelines to all election stakeholders.
… According to the document – Election Cybersecurity: Challenges and Opportunities – a democratic society needs a well-protected election lifecycle, from the maintenance of the electoral register and the public political campaigning process to the actual voting and the delivery of the results.


Interesting.
Is Digital Forensics Effectively Joining the Dots in Today’s Corporate Crime Scenes?
… Resolving complex corporate crimes requires tech-savvy sleuthing, and digital forensics does exactly that. It broadly covers identification, evaluation, examination, and peer review of computer or mobile device related artifacts. The coverage however continues to evolve with the emergence AI (Artificial Intelligence) and IoT (Internet of Things) enabled platforms, high security mobile devices, and other overarching trends in the technology world.
The insights presented in the article are based on a recent research study on Digital Forensics Market by Future Market Insights.


A culture that is not too concerned with accuracy (facts) will repeat this failure every time.
Facebook admits 18% of Research spyware users were teens, not <5 font="">
Facebook has changed its story after initially trying to downplay how it targeted teens with its Research program that a TechCrunch investigation revealed was paying them gift cards to monitor all their mobile app usage and browser traffic. “Less than 5 percent of the people who chose to participate in this market research program were teens” a Facebook spokesperson told TechCrunch and many other news outlets in a damage control effort 7 hours after we published our report on January 29th. At the time, Facebook claimed that it had removed its Research app from iOS. The next morning we learned that wasn’t true, as Apple had already forcibly blocked the Facebook Research app for violating its Enterprise Certificate program that supposed to reserved for companies distributing internal apps to employees.
… In the response from Facebook’s VP of US public policy Kevin Martin, the company admits that (emphasis ours) “At the time we ended the Facebook Research App on Apple’s iOS platform, less than 5 percent of the people sharing data with us through this program were teens. Analysis shows that number is about 18 percent when you look at the complete lifetime of the program, and also add people who had become inactive and uninstalled the app.”


Now that they have your attention…
Ireland's Data Protection Commission Reports Multiple GDPR Investigations on Tech Giants
Ireland's Data Protection Commission (DPC), headed by the Commissioner for Data Protection, Helen Dixon, has published its first annual report since the General Data Protection Regulation (GDPR) came into force in May 2018. It shows that Europeans are taking their new privacy rights very seriously. In the five months of 2018 pre-GDPR, the DPC received 1,249 privacy complaints. In the seven months post-GDPR, it received a further 2,864. The total of more than 4,000 complaints in 2018 is up from less than 1000 in 2015.
The section of the report (PDF) most relevant to Americans and American firms operating in Europe, however, is Section 7: Technology Multinationals Supervision.


Perhaps a good collection of bad examples?
Thailand passes internet security law decried as 'cyber martial law'
Thailand’s military-appointed parliament on Thursday passed a controversial cybersecurity law that gives sweeping powers to state cyber agencies, despite concerns from businesses and activists over judicial oversight and potential abuse of power.
The Cybersecurity Act, approved unanimously, is the latest in a wave of new laws in Asian countries that assert government control over the internet.
… The law allows the National Cybersecurity Committee (NCSC) to summon individuals for questioning and enter private property without court orders in case of actual or anticipated “serious cyber threats.”
An additional Cybersecurity Regulating Committee will have sweeping powers to access computer data and networks, make copies of information, and seize computers or any devices.
Court warrants are not required for those actions in “emergency cases,” and criminal penalties will be imposed for those who do not comply with orders.
… Legislators also unanimously passed the Personal Data Protection Act, intended to imitate the European Union’s General Data Protection Regulation (GDPR).


Update your toolkit.
Wireshark 3.0.0 Released
The Wireshark Foundation on Thursday announced the general availability of Wireshark 3.0.0, the newest release of the popular open-source packet analyzer.
The latest version fixes a handful of bugs and introduces roughly two dozen new features or significant updates to existing features.


Thursday, February 28, 2019

California is contagious?
Proposed Data Privacy Act for Washington State Could Be a Game-Changer
Inspired by the example of the European General Data Protection Regulation (GDPR), Washington State is now considering a comprehensive data privacy act that would protect the personal information of its citizens. If the new Washington Privacy Act (SB 5376) passes the state legislature this year, it would make Washington only the second state in America to adopt a comprehensive data privacy law.
… In fact, much of the language used within the Washington data privacy act is almost exactly the same as that found within the GDPR, especially when it comes to the definition of “personal data” and the notion of which protections should be offered to consumers as a fundamental basis of security and privacy.
With an emphasis on protecting personal information, the Washington data privacy act gives state residents several key rights, including the right to the deletion of data; the right to request any data errors to be corrected; the right to receive a personal copy of any personal data collected by a company in electronic format; and the right to withdraw consent from any personal data being processed.


(Related)
FPF Comments on the Washington Privacy Act, SB 5376
Today, the Future of Privacy Forum submitted comments to the Washington State Senate Ways & Means Committee on the proposed Washington Privacy Act, Senate Bill 5376. FPF takes a “neutral” position regarding the Bill, and makes a few important points.


Should Alexa think like a doctor or like a lawyer?
Seen on Foley Hoag’s Security, Privacy, and the Law blog:
Partner Colin Zick and Associate Jeremy Meisinger presented to the Massachusetts Health Information Management Association on the legal issues presented by the continued development of voice technology in healthcare. Click here to download the slides.


Why not a simple Traffic Robot? Don’t tie down a human, drop off a sensor loaded automaton and we’re good until the lights come back on.
Waymo Car AI Obeys Traffic Cop Hand Signals
Self-driving cars need to cope with every situation a human driver can, and that includes faulty lights at a junction being replaced with a traffic cop giving hand signals to follow.


A most interesting article. Clausewitz is too old (1832), let’s use Sun Tzu (500BC?) instead.
Why we should stop teaching Clausewitz


Could prove useful.
BillTrack50 is available for everyone to research state and federal legislation and legislators – free
“BillTrack50 is a free service for citizens to look up information about federal and state bills and legislators. Register for a free account to start searching right away. We also provide tools appropriate for professionals to help track bills, and to help organizations share important information on their own website. To see how the free and paid services compare, see our comparison matrix.”


Wednesday, February 27, 2019

A war, by any other name, would smell as sweet.
US Cyber Command attacked Russian troll farm on Election Day 2018
The United States Cyber Command launched an offensive campaign to silence one of Russia’s most notorious troll operations on the day of the 2018 midterm elections, according to a new report by The Washington Post. The operation targeted the Internet Research Agency, a private company linked to the Kremlin and often used for disinformation campaigns.
The US operation seems to have taken the IRA entirely offline during Election Day, to the point that many employees complained to systems administrators that they were unable to access the internet, according to the Post’s sources.
… It’s one of the most aggressive publicly reported campaigns the cyber command has yet taken, and the legal status of such actions remains in flux. In theory, infrastructural attacks against agents of a foreign government could have significant diplomatic repercussions, and run the risk of being taken as an act of war. But in practice, these actions are rarely officially attributed and political blowback is typically minimal.


The official database of the Ministry of Silly Walks? Every ache and pain is reflected in my ‘silly walk.’
Chinese police test gait-recognition technology from AI startup
South China Morning News: “You can tell a lot of things from the way someone walks. Chinese artificial intelligence start-up Watrix says its software can identify a person from 50 metres away – even if they have covered their face or have their back to a camera – making it more than a match for Sherlock Holmes. Known as gait recognition, the technology works by analysing thousands of metrics about a person’s walk, from body contour to the angle of arm movement to whether a person has a toe-in or toe-out gait, to then build a database. “With facial recognition people need to look into a camera – cooperation is not needed for them to be recognised [by our technology],” said Huang Yongzhen, co-founder and chief executive of Watrix, in an interview in Beijing.
Features like this have given Watrix an edge in catching runaway criminals, who tend to avoid surveillance, said Huang. Police on the streets of Beijing, Shanghai and Chongqing, have already run trials of gait recognition technology, said Huang, and the company officially launched its 2.0 version last week, which supports analysis of real-time camera feeds at a mega-city level. “We are currently working with police on criminal investigations, such as tracking suspects from a robbery scene,” said Huang, who was dressed all in black for the interview in his company office. “Currently, China has about 300,000 wanted criminals on the loose and counting. [Our software’s] database includes those with a prior gait record…”


Self-driving fighters.
Avalon 2019: Boeing to partner with Australia on development of multimission unmanned aircraft system
Boeing and Australia's Department of Defence (DoD) are to partner in developing a concept demonstrator for a large unmanned aircraft system (UAS) that will support and protect air combat missions.
… Dr Shane Arnott, director of Boeing's Phantom Works International, said system development had been under way for some time, but declined to say for how long.
The first flight will take place in Australia and is scheduled for 2020. The model unveiled at Avalon was representative of the intended flight vehicle, he said.
Although the platform would be powered by a single light commercial jet engine to save costs, "it will need to take off from the same runways and run the same speeds" as the aircraft with which it was teamed.
The system is not remotely piloted but will be semi-autonomous and controlled from both the ground and the air, he explained. "The intention is the teaming system will be an extension of the air power assets that it will be supporting," Arnott explained.


I have concerns.
Is war coming to South Asia?
… On February 26, the Indian military launched what it said were retaliatory air raids which allegedly destroyed a "terrorist" training camp in Pakistan's Khyber Pakhtunkhwa province. Pakistan for its part also responded with air raids across the line of control (LoC) which separates Indian- from Pakistan-administered Kashmir and claims to have downed two Indian fighter jets.
Military standoffs or escalations between India and Pakistan are not new, nor is the use of military means to settle scores. However, what sets this round of escalation apart is that this is the first time since the 1971 Indo-Pakistani war that the two countries attack targets deep within each other's territories.


Tuesday, February 26, 2019

Everybody’s doing it. Not just evil hackers.
Huawei Frightens Europe's Data Protectors. America Does, Too
A foreign power with possible unbridled access to Europe’s data is causing alarm in the region. No, it’s not China. It’s the U.S.
As the U.S. pushes ahead with the “Cloud Act” it enacted about a year ago, Europe is scrambling to curb its reach. Under the act, all U.S. cloud service providers from Microsoft and IBM to Amazon – when ordered – have to provide American authorities data stored on their servers regardless of where it’s housed. With those providers controlling much of the cloud market in Europe, the act could potentially give the U.S. the right to access information on large swaths of the region’s people and companies.
… The Cloud Act (or the “Clarifying Lawful Overseas Use of Data Act”) addresses an issue that came up when Microsoft in 2013 refused to provide the FBI access to a server in Ireland in a drug-trafficking investigation, saying it couldn’t be compelled to produce data stored outside the U.S.
The act’s extraterritoriality spooks the European Union – an issue that’s become more acute as trans-Atlantic relations fray and the bloc sees the U.S. under Trump as an increasingly unreliable ally.


For my Computer Security students.
Practitioner’s Guide for Assessing the Maturity of IoT System Security
The Industrial Internet Consortium® (IIC™), now incorporating OpenFog, announces the Security Maturity Model (SMM) Practitioner’s Guide, which provides detailed actionable guidance enabling IoT stakeholders to assess and manage the security maturity of IoT systems.


(Related)
European Telecommunications Standards Institute Publishes New IoT Security Standard
On February 19, the European Telecommunications Standards Institute (ETSI) published the ETSI TS 103 645 V1.1.1 – or more simply, a high-level outcome-focused standard (PDF) for cybersecurity in the consumer-oriented Internet of Things (IoT).
… The cybersecurity provisions are provided in section 4 of the standard. There are thirteen in total, some being simple statements and others comprising multiple subsections. For example, the total of provision 4.1 requires little more than its heading: "No universal default passwords."


Too useful to stop, so we’d best figure out how to do it correctly.
Jeffrey C. Skinner and Craig A. Newman of Patterson Belknap write:
The use of biometric technology is fast becoming the next big thing in privacy litigation. There was last month’s decision by the Illinois Supreme Court that upheld a consumer’s right to sue companies for collecting biometric data – such as fingerprints and iris scans – without first disclosing how such information will be used. See our blog on that ruling here.
And now, the debate surrounding the use and collection of biometric data has expanded beyond challenging the biometric collection practices in the private sector, to challenging the practices of state and local governments including law enforcement.
In Center for Genetics and Society v. Becera, a lawsuit filed late last year in California state court, two nonprofit organizations and an individual sued the state of California, challenging its DNA Fingerprint, Unsolved Crime and Innocence Protection Act (the “DNA Act”). The DNA Act authorizes the retention of DNA samples collected from people arrested on suspicion of a felony.
Read more on Data Security Law Blog.


What would a few thousand carefully worded discovery requests do to a small firm?
Californians could sue companies over privacy violations
State officials proposed a new amendment to the California Consumer Privacy Act (CCPA) on Monday that would allow consumers to sue companies that violate the new law. Currently, consumers can only file a lawsuit if they're victims of a data breach and only when the state's department of justice has decided not to sue on consumers' behalf.
… James P. Steyer, CEO of Common Sense, a non-profit organization that promotes safe technology use, said the amendment will take some of the burden of enforcing and monitoring violations off the attorney general's plate.
"Companies with endless resources will do everything they can to make it difficult for the AG," Steyer said in a statement. "By allowing consumers their own right to take action to hold bad actors accountable for violating their privacy, this law adds needed enforcement teeth to CCPA and Common Sense is firmly in support."
The amendment would also remove the current waiting period that gives businesses 30 days to attempt to remedy a violation and retract any exposed data from public view to avoid penalties.
… This new amendment follows legislation proposed on Thursday that would require companies to notify California residents when their passport, passport card or green card numbers are compromised in data breaches. It would also require customers be notified of compromised biometric information such as fingerprints.


(Related) Some topics that need discussion?
You’re Invited to an In-Person Event: CCPAnow: Understanding the Challenge Ahead And What You Should Be Doing Now
A few key topics that will be addressed are:
  • How should you interpret key definitions like “personal information,” “sale,” “third party,” and “business” when operationalizing the CCPA?
  • How far does a business have to go to implement a consumer’s opt-out of sales to third parties?
  • How will the financial incentives and anti-discrimination provisions actually work when consumers exercise their rights?
  • What is happening in the California Office of the Attorney General’s rulemaking process once the March 8th deadline for written comments has passed?


(Related)
How important is your privacy?
Axios: “…A full 81% of consumers say that in the past year they’ve become more concerned with how companies are using their data, and 87% say they’ve come to believe companies that manage personal data should be more regulated, according to a survey out Monday by IBM’s Institute for Business Value. Yes, but: They aren’t totally convinced they should care about how their data is being used, and many aren’t taking meaningful action after privacy breaches, according to the survey. Despite increasing data risks, 71% say it’s worth sacrificing privacy given the benefits of technology…”


Lawyers recommending surveillance?
Joe Cadillic writes:
Arizona State University (ASU) which spent $307 million to renovate Sun Devil Stadium has learned a lot about Smart City surveillance.
ASU used facial recognition to spy on alumni, students, faculty and families. And now they want to share what they learned by bringing it to a stadium or city near you.
An article in the Tech Republic revealed that Sun Devil Stadium and Croke Park in Ireland used facial recognition cameras to spy on fans.
Read more on MassPrivateI.


My students would never make such an assumption!


Monday, February 25, 2019

With great power comes great responsibility. I didn’t think we were quite there yet.
Federal judge finds male-only military draft unconstitutional
… Miller, who was appointed to the court by President George W. Bush in 2006, noted that the Supreme Court upheld excluding women from the draft in 1981 because women were excluded from combat duty. Because that prohibition was lifted in 2015, he wrote, excluding them from registering for the draft made no constitutional sense.


...and a few Oscar winners?
Thoughtful Entertainment Streaming now for free with your library card
kanopy – Over 30,000 films entirely free with a library card from participating libraries – “The films that truly resonate with us do more than just entertain. They inspire us, enrich us, and challenge our perspectives. Kanopy ensures that these films reach viewers around the world. We stream thoughtful entertainment to your preferred device with no fees and no commercials by partnering with public libraries and universities. Everyone from film scholars to casual viewers will discover remarkable and enriching films on Kanopy. Log in with your library membership and enjoy our diverse catalog with new titles added every month…”


Sunday, February 24, 2019

The long, long, long view
Google’s Hope and Dreams In India
… In 2011, Reliance, whose core business was oil and infrastructure, decided to build a vast broadband network, a business in which it had no experience but plenty of rivals. It had acquired a telecom company that owned mobile spectrum licenses, and it muscled in on its competitors. Barely 28 million Indians then owned smartphones. Reliance aimed to blanket India with broadband coverage, which was available only in big cities. After decades building pipelines and refineries, Reliance erected 220,000 mobile towers across India, often building more than 700 in a single day. In all, the project cost more than $30 billion.
In September 2016 it launched the Reliance Jio telecom network, offering people free mobile data for the first six months. Indians stampeded to grab the offer. Reliance Jio signed 100 million subscribers within six months and 250 million by its second anniversary last September. Its cheap plans set off a price war and drove down India’s data prices, from about $4.50 a gigabyte in 2016 to a rock-bottom 15¢ now, cutting deeply into competitors’ profits. For Reliance the pricing proved a masterstroke, establishing itself as a key phone and Internet service provider. Reliance Jio now sells $20 phones, and it is rolling out connected devices for cars, TV monitors, and home appliances.
… For Google, the disruption is a potential gold mine. Together, Reliance Jio’s network and Prime Minister Modi’s policies have cracked open markets that until now have been out of reach, or too small to be worth the investment. In 2017, shortly after Jio’s launch, Google created its first-ever digital payments app, Tez, seizing on the millions of Indians who were suddenly making digital payments. Last year, it renamed the app Google Pay. It now has about 40 million monthly active users in India, and is available in 29 countries, including the U.S., with about $60 billion in transactions in 2018, according to Google.


My students will need to understand how this works.
A guide to protecting AI and machine learning inventions
… The European Patent Office has recently amended its ‘Guidelines for Examination’ by including a new section containing advice about how patents related to AI and machine learning technologies should be assessed. The guidance clarifies that whilst algorithms are regarded as ‘computational’ and abstract in nature, which means they are not patentable per se, once applied to a technical problem they may become eligible for patent protection. Beneficially, the approach outlined in the guidance is similar to that currently used to assess the patentability of computer-implemented inventions.
To clarify, one of the keys to patentability lies in an invention’s ‘technical effect’. If an AI or machine learning invention is shown to have an effect in a real-world application, it is likely to be deemed patentable under the European Patent Convention