Tuesday, May 06, 2008

I can steal it for you wholesale!

http://www.pogowasright.org/article.php?story=20080506081942789

Finjan Discovers Compromised Business & Customer Data of 40 Top-Tier Global Businesses

Tuesday, May 06 2008 @ 08:19 AM EDT Contributed by: PrivacyNews News Section: Breaches

Finjan Inc., a leader in secure web gateway products, today announced its discovery of a server controlled by hackers (Crimeserver) containing more than 1.4 Gigabyte [less than I have on my thumb drive Bob] of business and personal data stolen from infected PCs. The data consisted of 5,388 unique log files. Both email communications and web-related data were among them.

The compromised data came from all around the world and contained information from individuals, businesses, as well as renowned organizations, including healthcare providers.

To illustrate the scope; the server contained among others 571 log files from the US, 621 from Germany (DE), 322 from France (FR), 308 from India (IN), 232 from Great Britain (GB), 150 from Spain (ES), 86 from Canada (CA), 58 from Italy (IT), 46 from the Netherlands (NL), and 1,037 from Turkey (TR).

Due to the sheer impact, Finjan followed its company guidelines and promptly notified over 40 major international financial institutions [It's not quantity, it'a quality. Bob] located in the US, Europe and India whose customers were compromised as well as various law enforcements around the world.

The report contains examples of compromised data that Finjan found on the Crimeserver, such as:

  • Compromised patient data

  • Compromised bank customer data

  • Business- related email communications

  • Captured Outlook accounts containing email communication

To download the report, please visit http://www.finjan.com/mpom

Source - PR Newswire

[From the Newswire article:

Since the stolen data was left unprotected on the Crimeserver, without any access restrictions or encryption, the data were freely available for anyone on the web, including criminal elements. [Tisk, tisk. Bad OpSec or sample data? Bob]


Is this automatically a terrorism case? Will similar risk apply when RealID is fully implemented?

http://www.pogowasright.org/article.php?story=20080506081227135

FBI notifies customers of Atlanta visa service

Tuesday, May 06 2008 @ 08:12 AM EDT Contributed by: PrivacyNews News Section: Breaches

The FBI is notifying as many as 1,000 customers of a metro Atlanta travel visa service that they may be victims of identity theft.

Warren Fowler, an employee of International Visa Service in Sandy Springs, has been arrested and charged with stealing the personal information of people who were applying for a passport. Fowler allegedly sent the information to his brother, Alvin Fowler, in Miami, who is accused of selling the identities for up to $7,500 each. Alvin Fowler is in federal custody.

Source - WRDW


Fortunately, the Zip was still Locked...

http://www.pogowasright.org/article.php?story=2008050605535628

NC: Officials recover stolen tax information (update)

Tuesday, May 06 2008 @ 05:53 AM EDT Contributed by: PrivacyNews News Section: Breaches

Law enforcement officials in Wingate have recovered personal financial information belonging to more than 400 taxpayers that was stolen last month.

The Iredell County Tax Collector’s Office said in a news release that a shipment of processed tax payments and unprocessed items that was reportedly stolen from a courier April 22 in Charlotte had been found and secured.

Officials said the bags did not appear to have been opened.

Source - statesville.com


The joy of databases – from the county that gave us “Big Brother.” A 40 second video with the sounds of Black Helicopters, police sirens, attack dogs, and a polite voice to remind you to pay you TV License, because...

http://digg.com/television/The_BBC_knows_where_you_live_its_all_in_the

The BBC knows where you live; its all in the

liveleak.com — Wow, is this real or fake? I love the veiled threats...fantastic! What do they do to you if you fail to license your TV? Do they send out the bone-crushers? Do folks show up at your door and take your TV?

http://www.liveleak.com/view?i=8ee_1210010683


An interesting resolution.

http://yro.slashdot.org/article.pl?sid=08/05/05/1617230&from=rss

US Court Orders Company to Use Negative Keywords

Posted by ScuttleMonkey on Monday May 05, @01:11PM from the negative-ghostrider-the-pattern-is-full dept.

A US court has ordered a firm to utilize negative adwords in their internet advertising.

"Orion Bancorp took Orion Residential Finance (ORF) to court in Florida over ORF's use of the word 'Orion' in relation to financial services and products, arguing that it had used the term since 2002 and had held a trade mark for it since then. [...] The judge in the case went further, though, restraining ORF from 'purchasing or using any form of advertising including keywords or "adwords" in internet advertising containing any mark incorporating Plaintiff's Mark, or any confusingly similar mark, and shall, when purchasing internet advertising using keywords, adwords or the like, require the activation of the term "Orion" as negative keywords or negative adwords in any internet advertising purchased or used.'"

[From the article:

By 'negative adword', the judge is referring to the fact that keyword advertising systems allow someone to instruct the system never to display their advert when a certain term is searched for, as well as to pay to have their ad displayed when a certain term is searched for.

... See: The ruling (9-page / 29KB PDF)


Might make for an interesting ethical discussion.

http://www.pogowasright.org/article.php?story=20080506061203573

Using cell phones to find missing persons pushes law

Tuesday, May 06 2008 @ 06:12 AM EDT Contributed by: PrivacyNews News Section: Businesses & Privacy

The call came in to police just after midnight April 16.

Hours before, a distraught young man had phoned his mother, hinting he wanted to kill himself. When he didn't meet her as planned, she telephoned Seattle police and reported her son missing.

Because of increasing advances in technology, officers were able to find the missing man's cellular phone using his wireless network. Two hours after he was reported missing, the man was found alive but unwell lying on his desk and taken to University Hospital for a psychological evaluation.

... "All the officer needs to do is confirm to us that an exigent circumstance exists," she said.

No legal challenges have been filed related to cell locater technology in missing persons cases. But privacy rights advocates say unambiguous guidelines are needed to ensure that the technology isn't misused.

Source - Seattle Post-Intelligencer hat-tip, slashdot

[From the article:

"It's a very, very small percentage of missing persons cases where it turns out that a crime has been committed," Rahr said.

... Masamitsu said Verizon, like other cellular providers, requires detailed follow-up reports from investigators. But she said the company doesn't conduct any independent review of the requests before releasing location information.

"All the officer needs to do is confirm to us that an exigent circumstance exists," she said.


Another ethical question?

http://www.eweek.com/c/a/Security/Kraken-Botnet-Infiltration-Triggers-Ethics-Debate/

Kraken Botnet Infiltration Triggers Ethics Debate

By Ryan Naraine 2008-05-01

Researchers seize control of one of the world's largest spam-spewing botnets, but there is disagreement about what should happen next.

Researchers at TippingPoint Technologies' Digital Vaccine Laboratories have found a way to infiltrate and seize control of one of the world's largest spam-spewing botnets, a breakthrough that has ignited an intense debate over the ethics of "cleaning" infected computers.

... The ability to infiltrate and seize control of Kraken's C&C mechanism left the company with an ethical dilemma that has prompted a discussion of whether infected computers used in denial-of-service attacks and spam runs should be cleansed without the owners' consent.

"On the technical side, we have proven that it can be done. From our proof-of-concept, it would have been one more click of a button to shut down the communication between the people sending commands to these [infected] computers," Pierce said.

... David Endler, director of security research at TippingPoint, is on the other side of the fence. "The reality is that you really don't know what you're modifying," Endler said in an interview. "It's a very tricky situation. What if that end-user system is performing a critical function? What if that target system is responsible for someone's life support? Who is to say what is more beneficial? It really is a moral and a legal quandary."


First, get their attention...

http://www.f-secure.com/weblog/archives/00001431.html

BBB Case #947344536

Posted by Mikko @ 16:05 GMT

We're seeing some new BBB trojan attacks going around.

This attack method is well-known and has been occurring for months: A high-level executive [Always target the most vulnerable... Bob] inside an organization receives an e-mail that mentions a complaint supposedly made to the Better Business Bureau (USA). The e-mail appears to be credible and links to a site in order to download the complaint. The download claims to require IE and ActiveX in order to succeed. Once ActiveX is enabled, the sites drops a backdoor on the system.

The message looks like this:

... The message links to a page under us-bbb.com (the real BBB site is at us.bbb.org).


For my computer security students.

http://news.yahoo.com/s/nm/20080502/od_nm/japan_porn_odd_dc;_ylt=AgStIVFU1Uyx7IdnqesY7yOs0NUE

Official suspended for surfing porn at work

Reuters Fri May 2, 11:09 AM ET

TOKYO (Reuters) - A city bureaucrat in western Japan was suspended from his job after officials discovered he visited porn websites at work almost every day, often spending hours [Interesting that no one noticed a lack of productivity. Perhaps he performed as well as any government employee? Bob] gazing at nude photos, a city official said.

... Angered citizens called city hall all day on Friday, saying the suspension was not enough, he added. [I wonder if there would be as much anger in the US? Bob]

The city only found out about his activities in February when it noticed that his computer had picked up the same virus repeatedly from the sites, Ueyama said. [Better than not noticing at all... Bob]


A safer way to find your porn? What is their liability for a “false positive?”

http://www.techcrunch.com/2008/05/05/yahoo-flags-malware-sites-in-search-results/

Yahoo To Flag Malware Sites In Search Results

Michael Arrington May 5, 2008

Tomorrow Yahoo will launch a partnership with McAfee and will integrate their Site Advisor malware scanning product into Yahoo search.

The most dangerous websites are simply being removed from search results. Yahoo is also flagging less dangerous offending sites to warn users of specific problems that have been reported from those sites. Example warning messages include “Warning: Unsolicited E-mails” and “Warning: Dangerous Downloads.”


For Security Managers. Another option for secure communications?

http://freenetproject.org/news.html

24th Apr, 2008 -

Freenet 0.7.0 release candidate 2 now available

Freenet version 0.7 Release Candidate 2 is now available for public testing. Release Candidate 2 features many bugfixes and a number of usability improvements.

Freenet is a global peer-to-peer network designed to allow users to publish and consume information without fear of censorship. To use it, you must download the Freenet software, available for Windows, Mac, Linux and other operating systems. Once you install and run Freenet, your computer will join a global, decentralized P2P network. [and likely be blocked by your ISP for sharing copyrighted music? Bob] You will be able to publish and consume information anonymously, either through your web browser, or through a variety of third party applications.

Freenet 0.7 is a ground-up rewrite of Freenet. The key user-facing feature in Freenet 0.7 is the ability to operate Freenet in a "darknet" mode, where your Freenet node will only talk to other Freenet users that you trust. This makes it much more difficult for an adversary to discover that you are using Freenet, let alone what you are doing with it. 0.7 also includes significant improvements to both security and performance.

Freenet 0.7 RC2 can be downloaded from: http://freenetproject.org/download.html


One of those business models that couldn't possibly work...

http://www.news.com/8301-13577_3-9936896-36.html?part=rss&subj=news&tag=2547-1_3-0-5

A billion-dollar valuation for LinkedIn?

Posted by Caroline McCarthy May 6, 2008 5:58 AM PDT

On Monday, reports surfaced that business social network LinkedIn is likely looking to raise a round of venture capital (rather than find a corporate parent).

TechCrunch reports that investment bank Allen & Co. is hoping to help LinkedIn pull in that funding at a $1 billion valuation.

... The average user of LinkedIn (there are 20 million total) is reportedly 41 years old and makes about $110,000 annually.

That's made it possible for the social network to charge advertisers $75 per thousand impressions, which is almost unheard of in the social-media world.


To free, or not to free...

http://www.nytimes.com/2008/05/06/technology/06wifi.html?_r=1&partner=rssnyt&emc=rss&oref=slogin

Free Wi-Fi, but Not for All

By SUSAN STELLIN Published: May 6, 2008

The battle between free and paid wireless Internet access is starting to look like a draw. Or more accurately, a third variation is winning — a combination of the two.

... Starbucks is probably the biggest example of that model. In February, the company announced plans to switch to AT&T from T-Mobile as the Internet provider in its 7,000 stores.

When AT&T takes over, customers who use their Starbucks card once a month will get two hours of free Wi-Fi access each day. Otherwise, that same time period will cost $3.99, or $19.99 for a monthly unlimited access plan.

... Denver International Airport switched from a paid to an ad-supported model last November, and has already seen use increase from 600 connections a day to more than 5,000.

... That ad revenue slightly exceeds what the airport used to earn from its share of user fees ($7.95 for 24 hours of access), according to Jim Winston, the airport’s director for telecommunications. [See? Free is good! Bob]


Apparently, it is easy to screw up. Checklists might help...

http://ralphlosey.wordpress.com/2008/05/04/aba-litigation-section-reacts-to-the-qualcomm-case-and-recommends-e-discovery-checklists/

ABA Litigation Section Reacts to the Qualcomm Case and Recommends e-Discovery Checklists

The Litigation Section of the American Bar Association has published an online article on Qualcomm v. Broadcom. Written by Kristine L. Roberts, Litigation News Associate Editor, the article is significant for its glimpse into the thinking of ABA leaders on electronic discovery abuses.


What's in your coffin? (Not every untapped market will be lucrative...)

http://www.wired.com/techbiz/startups/news/2008/05/tributes

Monster.com Founder Starts Social Networking Site for the Dead

By Marty Graham 05.05.08 | 1:00 PM


How could I pass this one up?

http://digg.com/comics_animation/The_Simpsons_Compilation_of_Couch_Gag_Intros

The Simpsons - Compilation of Couch Gag Intros watch!

youtube.com — Love the Evolutionary Couch Gag...lots of good ones in the related videos here.

http://youtube.com/watch?v=aCld99SNg1o&feature=related

Monday, May 05, 2008

It's not always something as big as a laptop...

http://www.pogowasright.org/article.php?story=20080505063736778

Hospitals in Hong Kong lose data on 3,000 patients in thefts

Monday, May 05 2008 @ 06:37 AM EDT Contributed by: PrivacyNews News Section: Breaches

Data on more than 3,000 patients in Hong Kong public hospitals has been lost through the theft of computer memory sticks, officials said Monday.

Nine memory sticks have been stolen from five hospitals across the city of 6.9 million in the past year, the hospital authority's chief executive Shane Solomon said.

Source - Monsters & Critics

[From the article:

'It is not a matter of staff negligence,' he said. 'It is a matter of people seeing a USB stick sitting around in a computer and thinking 'I'll take that, thank you very much.''

[Of course it's negligence. Armed robbery may be unavoidable, creating portable information isn't. Bob]


...because... Slow week, only 24 new reports...

http://www.pogowasright.org/article.php?story=2008050506355247

Data “Dysprotection:” breaches reported last week

Monday, May 05 2008 @ 06:50 AM EDT Contributed by: PrivacyNews News Section: Breaches

A recap of incidents or privacy breaches reported last week for those who enjoy shaking their head and muttering to themselves with their morning coffee. This week, figure on at least two cups to get through the list.

Source - Chronicles of Dissent


Interesting, but not ground breaking.

http://www.phiprivacy.net/?p=360

May-5-2008

AHIMA Releases Privacy Roundtable Report

A new privacy and security report from four leading HIM experts is now available. In “Online, on Message, on Duty: Privacy Experts Share Their Challenges” four experts in health information privacy participated in a roundtable discussion on key issues related to the privacy and security of health information-and ways in which the industry may best address those issues. The report was released in conjunction with the American Health Information Management Association’s (AHIMA) fifth annual Health Information Privacy and Security Week April 13-19, established to raise public and professional awareness of issues related to the privacy and security of patient health information. The complete report is available at www.ahima.org/emerging_issues/2008PrivacyRoundtable.pdf.

Full story - Advance


Infrastructure choke point

http://www.bespacific.com/mt/archives/018254.html

May 04, 2008

Digital Directory for 800 Telephone Companies Sparks Concern

The Ultimate Little Black Book - One Firm Routes All Phone Calls in North America, by Ellen Nakashima, Washington Post.

  • "Sterling-based NeuStar is the carriers' digital directory for all phone calls in North America. More than 800 telephone companies have numbers in the database...NeuStar's databases are so powerful that the FBI a few years ago sought direct, unfettered access to one containing 310 million phone numbers in the United States and Canada. The telephone companies that pay NeuStar to run the database denied the FBI's request, but they did allow NeuStar to create a site where authorized law enforcement officials with court orders can obtain carrier information on telephone numbers. NeuStar is part of an evolving telecom industry that is creating caches of information attractive to the government without clear guidelines governing who may have access and under what circumstances. Its registries fall under international, U.S. government and trade association rules, including those set by the Federal Communications Commission."

[From the article:

And about one out of every four Internet transactions is routed using a NeuStar database, as NeuStar handles traffic for domains that include .biz, .us, .org and .info.

... Soon, they said, NeuStar expects to be providing digital directory service for about 85 percent of all wireless devices in the world.

NeuStar officials say the government has not sought direct access to any of its databases other than the one the FBI requested, which covered numbers kept by customers as they switched providers, called a ported number registry.

But Al Gidari, a lawyer representing wireless carriers, said other major telecom entities -- billing vendors, 911 emergency service providers and call center operators -- have databases the government might want to tap. "If the government wanted access to their databases, there are no clear procedures regulating that access as there are for phone companies," he said. "That's a danger."


CyberWar – the Neville Chamberlain years? How far is too far? When should we take concerted action? Does anyone believe the Chinese government is not involved?

http://it.slashdot.org/article.pl?sid=08/05/05/1211259&from=rss

China's Cyberwar Against India

Posted by CmdrTaco on Monday May 05, @08:40AM from the no-no-we're-cool-promise dept. Security

An anonymous reader writes

"China's cyber warfare army is marching on, and India is suffering silently. Over the past one and a half years, officials said, China has mounted almost daily attacks on Indian computer networks, both government and private, showing its intent and capability."

[From the article:

A quiet effort is under way to set up defence mechanisms, but cyber warfare is yet to become a big component of India’s security doctrine. Dedicated teams of officials — all underpaid, of course — are involved in a daily deflection of attacks. But the real gap is that a retaliatory offensive system is yet to be created.

And it’s not difficult, said sources. Chinese networks are very porous — and India is an acknowledged IT giant!


For my Computer Security class: How do you stop this?

http://www.pcworld.com/businesscenter/article/145449/100_email_bouncebacks_youve_been_backscattered.html

100 E-mail Bouncebacks? You've Been Backscattered.

Robert McMillan, IDG News Service Friday, May 02, 2008 4:10 PM PDT

The bounceback e-mail messages come in at a trickle, maybe one or two every hour. The subject lines are disquieting: "Cyails, Vygara nad Levytar," "UNSOLICITED BULK EMAIL, apparently from you."

You eye your computer screen; you're nervous. What's going on ? Have you been hacked? Are you some kind of zombie botnet spammer?

Nope, you're just getting a little backscatter -- bounceback messages from legitimate e-mail servers that have been fooled by the spammers.

Spammers like to put fake information in their e-mail messages in order to sneak them past e-mail filters. Because e-mail filters now just delete messages that come from nonexistent domains, the spammers like to make their messages look like they come from real e-mail addresses. That means, if your e-mail address has been published on the Web somewhere, you're a prime candidate for backscattering.

The spammer finds your address, or sometimes even guesses it, and then puts it in the "from" line of his messages, sending them out to hundreds of thousands of recipients. When the spam gets sent to an address that is no longer active, it can sometimes be bounced back ... to you.

Although Sophos estimates that backscatter makes up just two percent or three percent of all spam, antispam vendors say these messages are on the rise lately.

... Backscatter rarely hits more than one or two employees at the same time, so it isn't particularly disruptive. But it does worry users, he said. "It's mostly a psychological thing."

... Because backscatter comes from legitimate mail servers, it can cause special problems. In fact, some security researchers believe that the spammers have been intentionally sending messages that will be bounced back as a way to sneak around spam filters. That's because some mail servers bounce back the original message as part of their notice.

... At its worst the phenomenon can even wipe Internet servers off the map.

Last month, Stephen Gielda, president of Packetderm, upset a fraudster who was trying to use his anonymous Internet service. Soon his servers were inundated with a tidal wave of backscatter messages. At one point, he was being hit by 10,000 bounceback messages per second, enough to throttle the server's Internet connection.

... But the problem would largely disappear if server administrators configured their mail servers to immediately reject mail that is sent to nonexistent users, rather than accepting it and then bouncing it back to the faked addresses.


Ditto A list of crimes & criminals, including the prisons they are in.

http://www.infoworld.com/article/08/05/05/19FE-stupid-hackers-part2-youth-tease_1.html?source=rss&url=http://www.infoworld.com/article/08/05/05/19FE-stupid-hackers-part2-youth-tease_1.html

Stupid hacker tricks, part two: The folly of youth

Tech-savvy delinquents set the Net aflame with boneheaded exploits that earn them the wrong kind of fame

By Andrew Brandt May 05, 2008


Are these the stake in RIAA's heart? The best business models turn your passion into profit...

http://www.news.com/8301-10784_3-9934879-7.html?part=rss&subj=news&tag=2547-1_3-0-5

May 5, 2008 4:00 AM PDT

Music blogs: The new wall of sound

Posted by Greg Sandoval

... Now, the most popular blogs, such as Stereogum, BrooklynVegan, and Pitchfork, look less and less like Internet fanzines and more like tech start-ups.


Want to try it?

http://www.killerstartups.com/Web-App-Tools/AltaBlogscom---Quick-Easy-Free-Blog-Setup/

AltaBlogs.com - Quick, Easy, Free Blog Setup

... AltaBlogs.com is a site that lets users create their own blog. AltaBlogs.com makes it easy for you to start blogging away by giving you an easy set up for creating your blog. First you must make an account with AltaBlogs.com and then you can set up your blog. You can choose your blog domain name as well as blog title. You can choose to have your blog searchable on Google or keep it private. It is quick, simple and free to start your own blog at AltaBlogs.com.

http://altablogs.com/


Related. Who needs traditional music publishers?

http://digg.com/music/NIN_Gives_Away_New_Full_Length_Album_the_slip

NIN Gives Away New Full Length Album - the slip

theslip.nin.com — as a thank you to our fans for your continued support, we are giving away the new nine inch nails album one hundred percent free, exclusively via nin.com. the music is available in a variety of formats including high-quality MP3, FLAC or M4A lossless at CD quality and even higher-than-CD quality 24/96 WAVE.

http://theslip.nin.com/


Related? I think so.

http://www.nytimes.com/2008/05/05/business/media/05idg.html?_r=1&partner=rssnyt&emc=rss&oref=slogin

Publisher Tested the Waters Online, Then Dove In

By STEVE LOHR Published: May 5, 2008

... The biggest single step in the company’s online shift came on April 2, 2007, when the last print edition of InfoWorld appeared and it became a Web-only publication.

... Today, I.D.G. says, the InfoWorld Web site is generating ad revenue of $1.6 million a month with operating profit margins of 37 percent. A year earlier, when it had both print and online versions, InfoWorld had a slight operating loss on monthly revenue of $1.5 million.

... Without the physical limitations of print, Mr. Knorr said, it becomes easier to explore topics more deeply. InfoWorld presents a stable of bloggers, including 19 freelance writers, who are authorities in niches including data protection, green technology, open source software and cloud computing.


This is 1) a way to foil TSA laptop “inspections” 2) a way to steal all your important documents [Pick two]

http://www.killerstartups.com/Web-App-Tools/Ilockerorg---Store-Important-Documents/

Ilocker.org - Store Important Documents

The last time you had a locker may have been high school, but that doesn’t mean that using one now is anachronistic; you just have to find one to match your needs. Allow me introduce iLocker. iLocker is an online safe to store important text documents. The web application encrypts the text using a password of your choice and their own encryption method. Once the text is stored away, iLocker does not save any information linking you to the locker, including your name or password. The result is a totally secure, anonymous location to guard your most important documents and writings. Puts that old high school locker to shame, doesn’t it?

http://www.ilocker.org/home/


E-mail tool Wouldn't be necessary if Microsoft was aggressively adding features.

http://venturebeat.com/2008/05/04/xobni-the-email-organizer-for-outlook-launches-publicly/

Xobni launches email organizer for Outlook

Matt Marshall May 4th, 2008

Xobni, the San Francisco company we raved about last year that offers a way to better organize your email from Outlook, is launching publicly with its test version.

Its key feature is a sidebar in your inbox that shows you profiles of the people you’re corresponding with. It makes information easily accessible, such as their phone numbers, past correspondence and files you’ve exchanged with them. We mentioned last week its work to join Microsoft and Yahoo’s email offerings.

Sunday, May 04, 2008

The scope of access is where security went wrong. As my Hacking Class learns each new technique they can access parts of their final grade. Learn all the techniques, give yourself an “A” (There is no way to access other students' grades...)

http://www.chron.com/disp/story.mpl/front/5750954.html

Hackers change grades at Fort Bend ISD high school

Four Hightower students being investigated after scores were changed for 60

By ERIC HANSON Copyright 2008 Houston Chronicle

SUGAR LAND — Four high school students are being investigated on suspicion of breaking into the Fort Bend Independent School District's computer network and changing the grades of at least 60 students, according to court documents and school officials.

Investigators estimated the financial loss to the school district at more than $190,000, making the case a possible felony. [I'd love to see the justification for that number... Bob]

... School officials did not say if all the grades were improved or if the hackers gave some students lower grades. [Never mess with a geek! Bob]

... That discovery launched police on a lengthy cyber trail involving the use of sophisticated detection programs and the issuing of low-tech subpoenas. [Paper? Bob]


I wonder if any of my students are involved?

http://www.pogowasright.org/article.php?story=200805030817580

5,500 Argosy University students had data on stolen Sungard HE laptop (SunGard Update) (corrected)

Saturday, May 03 2008 @ 08:17 AM EDT Contributed by: PrivacyNews News Section: Breaches

Argosy University has notified; the Maryland Attorney General that the laptop stolen from a Sungard HE employee in March contained personal information including name, Social Security number, and in many cases, addresses, of 5,500 Argosy University students who may have applied for financial aid in 2001, 2002, and/or 2004.

Corrected at 12:33 pm to insert correct url to notification letter.

Related - previous coverage of the SunGard HE incident on PogoWasRight.org


Perhaps this will change the courses these law school students take? The sample “letter to victims” suggest they will notify Maryland residents only – or am I misreading it?

http://www.pogowasright.org/article.php?story=20080503082509618

Yeshiva University law students' personal information on stolen laptop (SunGard update)

Saturday, May 03 2008 @ 08:25 AM EDT Contributed by: PrivacyNews News Section: Breaches

Some students of Yeshiva University's Benjamin N. Cardozo School of Law had their personal information stolen when a laptop was stolen from a SunGard HE employee in mid-March. According to Yeshiva's notification to the Maryland Attorney General, information for a "small number of former students" included names, Social Security numbers, student loan identification numbers, other financial aid info, and other student information.

Related - previous coverage of the Sungard HE incident on PogoWasRight.org


Interesting. Who could this be?

http://www.pogowasright.org/article.php?story=20080503110202644

AU: WESTPAC recalls uo (sic) to 2000 Visa cards

Saturday, May 03 2008 @ 11:02 AM EDT Contributed by: PrivacyNews News Section: Breaches

WESTPAC has been forced to recall up to 2000 Visa cards after a security breach exposed customers to "high risk" of fraud.

The bank wrote to customers on April 22 telling them their account details may have been compromised and that their cards needed to be replaced.

A letter stated that because of the "high risk compromise to your account" customers' cards would be blocked if they did not contact the bank by April 29.

... She said the breach had taken place overseas.

Source - news.com.au

[From the article:

A Westpac spokeswoman said the breach was an example of "a common point of purchase compromise where a single vendor has broken security".

[This suggests that at least 2000 people used the Visa cards at the same vendor (same card swipe machine?) I can only think of an airline or perhaps someplace like Harrod's. No doubt we'll find out soon, if the “overseas” country has disclosure laws or a large number of customers in Maryland, New Hampshire or California. Bob]


This is actually good news. I doubt there are many organizations who would even look back this far. (Or is this an ongoing case and they just realized the Identity Theft potential?) The notification letter was scanned in upside down and no one seems to have noticed – fortunately you can “rotate” the image by clicking a button.

http://www.pogowasright.org/article.php?story=200805030844228

Purdue Pharma employees notified of security breach

Saturday, May 03 2008 @ 08:44 AM EDT Contributed by: PrivacyNews News Section: Breaches

Purdue Pharma, a privately held pharmaceutical company, notified the Maryland Attorney General on April 14 that they had recently learned that a "former employee accessed a disk containing personal information about individuals employed by Purdue Pharma and its associated U.S. companies prior to December 31, 2003 and attempted to email some of the information on the disk to another person."

The disk contained names, dates of birth, Social Security numbers and pension-related information on approximately 5,000 individuals.

In his letter [pdf] to the AG's office, David Long, Senior Vice President of Human Resources, reports that the employee kept the disk when his employment ended, in direct violation of the company's policies and standard confidentiality agreement. When the company discovered the unauthorized access, they demanded that the information be "deleted and returned to us." [Watch your language. Would you really want to receive a blank disk with a note saying “the data used to be here, but I deleted it?” Bob] They report that the original disk has been returned and that they believe that all copies of the information have been deleted and that there has been no misuse of the information.

The documentation submitted does not indicate when the unauthorized access occurred or when the employee terminated employment. The company discovered the unauthorized access in late March, 2008.

Purdue Pharma contracted with TrustedID to provide two years' services to those whose data were on the disk.


To err is human, to screw up this massively takes a bureaucracy...

http://www.pogowasright.org/article.php?story=20080503130505156

Hundreds of Laptops Missing at State Department, Audit Finds

Saturday, May 03 2008 @ 01:05 PM EDT Contributed by: PrivacyNews News Section: Breaches

Hundreds of employee laptops are unaccounted for at the U.S. Department of State, which conducts delicate, often secret, diplomatic relations with foreign countries, an internal audit has found.

As many as 400 of the unaccounted for laptops belong to the department’s Anti-Terrorism Assistance Program, according to officials familiar with the findings. [Terrorists like to steal these first... Bob]

The program provides counterterrorism training and equipment, including laptops, to foreign police, intelligence and security forces.

Source - CQ Politics hat-tip, Raw Story

[From the article:

Ironically, the Anti-Terrorism Assistance Program is administered by the State Department’s Bureau of Diplomatic Security (DS), which is responsible for the security of the department’s computer networks and sensitive equipment, including laptops, among other duties. It also protects foreign diplomats during visits here. [Doesn't that give you a warm fuzzy feeling? Bob]

... A senior IG official, asking not to be identified, said he could “not comment on ongoing work.” [You must be scared if you don't want to be identified as saying “No comment.” Bob]

... Hints of the State Department’s laptop losses first surfaced March 31 in an anonymous post at an obscure Web site frequented by employees of the Bureau of Diplomatic Security, called Dead Men Working. [Goodbye obscure. Bob]


Be very careful to ensure that your spokespeople know the facts. Nothing says “We're lying” like a number of contradictory statements –in writing!

http://www.pogowasright.org/article.php?story=20080504075258305

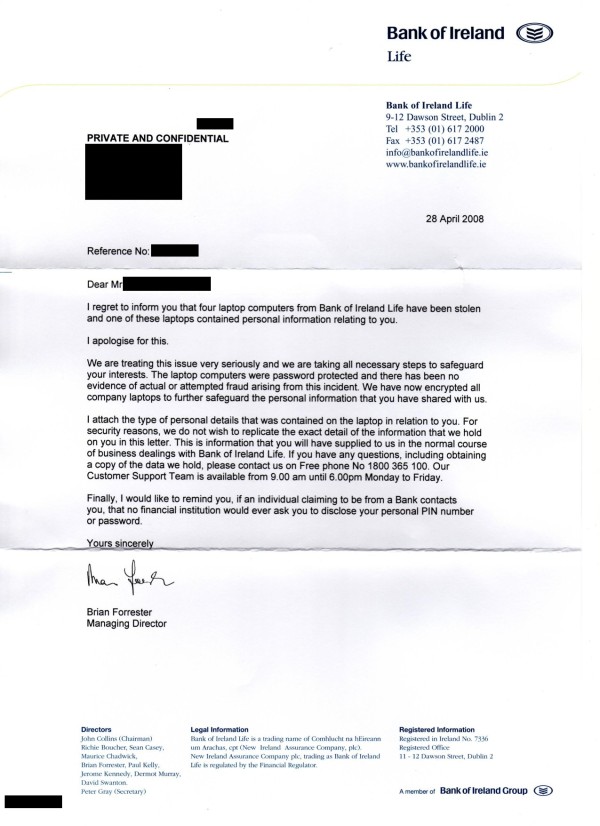
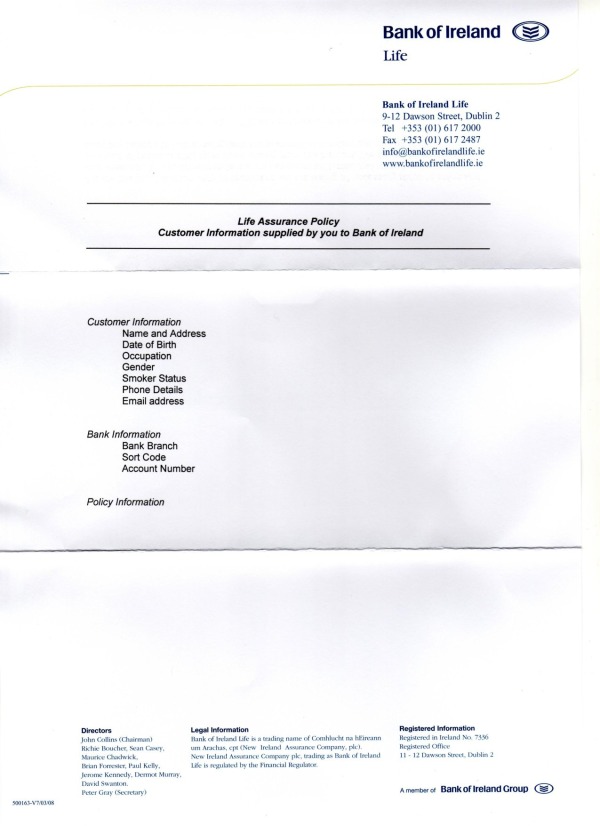
BoI data breach: a sample customer notification (follow-up)

Sunday, May 04 2008 @ 07:52 AM EDT Contributed by: PrivacyNews News Section: Breaches

More on the Bank of Ireland 30,000-customer data breach (which is up to 31,500 people by now — BoI promised to contact the “affected” customers by post, warning them that their data had been leaked. If you were wondering what those letters might look like, wonder no more. Here’s one, via a friend who found himself in this unenviable position:

Page 1 Page 2 [Not a hacker? You may need to link via the taint.org article Bob]

So it’s not just name, date of birth, and address — he notes that they’ve leaked ‘information on the current account I use to pay for the policy.’

Interestingly, he says that his life assurance policy was set up directly with their life assurance department, not via the local branch — which directly contradicts what BoI say on their website....

Source - taint.org

Note: if anyone received a letter from BoI that references medical information, please send a redacted copy to privacynews[at]pogowasright.org


Security is as security does. F. Gump “I want you photographers to note that this is the equipment we executed those spys for trying to photograph. Be sure to get my good side...”

http://news.slashdot.org/article.pl?sid=08/05/03/2231202&from=rss

An Inside Look At Iran's Nuclear Program

Posted by timothy on Saturday May 03, @06:39PM from the glowing-reviews dept. Power The Military Politics Science Technology

NotBornYesterday writes

"On April 8, Iranian President Mahmoud Ahmadinejad visited his country's secretive nuclear enrichment plant at Natanz for a photo op. What came out of this visit is a series of photos which have caused a fair amount of interest among western scientists. Shown in the photos are not only some of the inner workings of the plant and current generation of enrichment centrifuges, but also key components to newer generations of more effective centrifuges. Analysts are 'intrigued' not only by the technical revelations in the pictures, but also because Iran's Defense Minister Mostafa Mohammad Najjar accompanied Ahmadinejad through the facility."


War is hell

http://www.huffingtonpost.com/2008/05/03/unearthed-photos-reveal-h_n_99970.html

New Photos Reveal Horror Of Hiroshima (GRAPHIC IMAGES)

The Huffington Post May 3, 2008 02:04 PM

... Below, you'll find one of the photos from this collection. See the rest here. Warning: some of the images are graphic and will be difficult for some readers to view.


It's one of those silly databases geeks love.

http://digg.com/programming/The_Hello_World_Program_in_366_Programming_Languages

The "Hello World" Program, in 366 Programming Languages!

roesler-ac.de — "Hello World" is the traditional first program you write when learning a new language, first appearing in K&R's "The C Programming Language" book in 1978. Since then it has been implemented in almost every programming language on the planet. This collection has it in 366 coding languages (even LOLCode!) and 58 human ones! Is your favourite here?

http://www.roesler-ac.de/wolfram/hello.htm


For those of us who know Classical does not mean “Brittany Spears, the Early Years”

http://www.gramophone.co.uk/newsMainTemplate.asp?storyID=3020&newssectionID=1

Gramophone to launch revolutionary website

May 2 2008

... By September every word ever printed in Gramophone will be available for free as a fully searchable online archive – that’s hundreds and thousands of reviews, articles and interviews, by far the biggest archive of its kind.

... The new website, Gramophone.net, will be created in two stages. The first, the creation of the archive, will live alongside this existing website from early September. The start of 2009 will then see the creation of an all-new state-of-the-art website – where downloading, internet mail order and ticket-buying services will be linked to editorial – so visitors will be able to read reviews and features, listen to music samples and then if they wish, buy CDs or book tickets to live events.


Dennis has outdone himself... Instead of mere lists, he is now sending me lists of lists. That's good, because I plan to send you lists of my list of lists, so you can collect them and have lists of my lists of Dennis' lists of lists...

http://www.listverse.com/

Saturday, May 03, 2008

I don't know if I'd refer to breaches my employees didn't know about. (and other strange things...)

http://www.pogowasright.org/article.php?story=20080502131843517

UK: BP Memo Warns Of "Catastrophic" Risk Of Information Leaks

Friday, May 02 2008 @ 01:18 PM EDT Contributed by: PrivacyNews News Section: Breaches

PogoWasRight.org editor's note: this story contains references to severally previously unreported breached involving BP:

... The memo warns BP's employees of potentially "catastrophic" consequences if staff transfer sensitive data outside the company. Offering examples of such potentially harmful information leaks, the memo cites a U.S. Gulf of Mexico identity theft, the stealing of a U.K. laptop computer containing executive pay details, and the separate near-collapse of an Asia-Pacific deal.

In a Powerpoint presentation attached to the memo, seen by Dow Jones Newswires, the U.K. oil giant mentions a case in which "a laptop containing a number of highly sensitive documents, including salary details of some of BP's most senior executives, was stolen from an employee's car." The employee had gone dining at a restaurant close to BP's Sunbury office, which hosts its U.K. exploration and production activities.

[...]Finally, the document cites how a U.S. Gulf training contractor stole "BP employee identities to secure phones, loans and utilities."

Source - EasyBourse


One for the bookshelf (or I may actually read it)

http://www.pogowasright.org/article.php?story=2008050215505153

Solove: Understanding Privacy

Friday, May 02 2008 @ 03:50 PM EDT Contributed by: PrivacyNews News Section: Other Privacy News

Privacy lawyer Dan Solove has a new book out, Understanding Privacy. Here's the publisher's blurb on it:

Privacy is one of the most important concepts of our time, yet it is also one of the most elusive. As rapidly changing technology makes information more and more available, scholars, activists, and policymakers have struggled to define privacy, with many conceding that the task is virtually impossible.

In this concise and lucid book, Daniel J. Solove offers a comprehensive overview of the difficulties involved in discussions of privacy and ultimately provides a provocative resolution. He argues that no single definition can be workable, but rather that there are multiple forms of privacy, related to one another by family resemblances. His theory bridges cultural differences and addresses historical changes in views on privacy. Drawing on a broad array of interdisciplinary sources, Solove sets forth a framework for understanding privacy that provides clear, practical guidance for engaging with relevant issues.

Understanding Privacy will be an essential introduction to long-standing debates and an invaluable resource for crafting laws and policies about surveillance, data mining, identity theft, state involvement in reproductive and marital decisions, and other pressing contemporary matters concerning privacy.

You can Download the first chapter to get a sense of the book, which can be ordered from Amazon.com or Barnes & Noble


So much turmoil in only 15 years...

http://www.cnet.com/8301-13641_1-9933894-44.html?tag=bnpr

May 1, 2008 4:56 PM PDT

Happy 15th birthday, WWW

Posted by Adam Richardson Post a comment

Fifteen years ago yesterday, the World Wide Web became official and was put into the public domain.


An even more historical (older) computing milestone... (Notice that is remains virus free!) They plan to build a virtual Difference Engine – I hope to get a copy...

http://www.news.com/2300-1041_3-6238822-1.html?part=rss&tag=6238822&subj=news

The Victorian engine that could

May 2, 2008 3:43 PM PDT Caption text by Kara Tsuboi

Calling all history buffs: Charles Babbage's Difference Engine No. 2 is making its North American debut at the Computer History Museum in Mountain View, Calif.

A forward-thinking mathematician and engineer, Babbage designed the Difference Engine in 1847. His intent was to create an automated computing machine, but he was never able to turn his vision into reality.

Fast forward 150 years, and an impassioned Babbage expert and wealthy financier have teamed up to build Babbage's dream via a new exhibit running through next April. (Click here for related video)


Two for my Computer Security students...

http://www.bespacific.com/mt/archives/018245.html

May 02, 2008

NIST Computer Security Division 2007 Annual Report

"The NIST Computer Security Division...release of NIST Interagency Report (IR) 7442: Computer Security Division - 2007 Annual Report. This publication highlights the diverse research agenda that enabled the Computer Security Division to successfully respond to numerous challenges and opportunities in fulfilling its mission to provide standards and technology that protects information systems against threats to the confidentiality, integrity, and availability of information and services."


The HIPAA act was 1996. Guidelines in 2008. Implementation by 2020?

http://www.bespacific.com/mt/archives/018244.html

May 02, 2008

An Introductory Resource Guide to Implementing the Health Insurance Portability and Accountability Act

"NIST announces the release of the public draft of Special Publication 800-66 Revision 1, An Introductory Resource Guide to Implementing the Health Insurance Portability and Accountability Act (HIPAA) Security Rule (Draft). This Special Publication (SP), which discusses security considerations and resources that may provide value when implementing the requirements of the HIPAA Security Rule, was written to help educate readers about information security terms used in the HIPAA Security Rule and to improve understanding of the meaning of the security standards set out in the Security Rule, direct readers to helpful information in other NIST publications on individual topics the HIPAA Security Rule addresses, and aid readers in understanding the security concepts discussed in the HIPAA Security Rule. This publication does not supplement, replace, or supersede the HIPAA Security Rule itself. Comments on Draft SP 800-66 Revision 1 will be accepted through June 13, 2008."

Friday, May 02, 2008

“What, me hurry?” A. E. Newman

http://www.pogowasright.org/article.php?story=20080501195923906

UCSF waited six months before telling patients of data breach

Thursday, May 01 2008 @ 07:59 PM EDT Contributed by: PrivacyNews News Section: Breaches

Information on thousands of UCSF patients was accessible on the Internet for more than three months last year, a possible violation of federal privacy regulations that might have exposed the patients to medical-identity theft, The Chronicle has learned.

The information accessible online included names and addresses of patients along with names of the departments where medical care was provided. Some patient medical record numbers and the names of the patients' physicians also was available online.

The breach was discovered Oct. 9, but the medical institution did not send out notification letters to the 6,313 affected patients until early April, nearly six months later.

.... UCSF had shared information on its patients with a vendor, Target America Inc., which mines electronic databases amassing information about a nonprofit's potential or existing donors.

Source - San Francisco Chronicle

[From the article:

"The breach is a symptom, but the real ethics challenge is the extent to which health care institutions are tracking patients and their families for nonmedical reasons - for fundraising, marketing, advertising," Caplan said. "I don't think people are aware of the degree to which this is occurring, whether it's by a hospital or a nursing home or a hospice."


Do they really mean mimic? If so, why is this good news?

• verb (mimicked, mimicking) 1 imitate in order to entertain or ridicule. 2 (of an animal or plant) take on the appearance of (another) to deter predators or for camouflage. 3 replicate the effects of. Source: Compact Oxford English Dictionary of Current English

http://www.pogowasright.org/article.php?story=20080501171844580

(update) Analysis Reveals No Security Breach, No Personal Data Exposed At CU-Boulder

Thursday, May 01 2008 @ 05:18 PM EDT Contributed by: PrivacyNews News Section: Breaches

The University of Colorado at Boulder today announced that a forensic analysis of a computer suspected to have been compromised last week revealed no malicious software, and no exposure of student and staff private data.

"The analysis by our staff, working closely with the consulting firm of Applied Trust Engineering, revealed an interaction between two incompatible software programs that mimicked behavior consistent with malicious software," said Dan Jones director of IT Security at CU-Boulder.

Source - University of Colorado - Boulder

Related - Not hacked off, or into


The equivalent of asymmetric CyberWar?

http://www.securityfocus.com/news/11515?ref=rss

Radio Free Europe hit by DDoS attack

Dan Goodin, The Register 2008-05-01

Websites run by Radio Free Europe have been under a fierce cyber attack that coincided with coverage over the weekend of a rally organized by opposition to the Belarusian government.

The distributed denial of service (DDoS) attack initially targeted only the RFE's Belarus service, which starting on Saturday was inundated with as many as 50,000 fake pings every second, according the this RFE account. On Monday, it continued to be affected. At least seven other RFE sites for Kosovo, Azerbaijan, Tatar-Bashkir, Farda, South Slavic, Russia and Tajikistan, were also attacked but have mostly been brought back online.


Often level-headed recommendations, backed by actual thought!

http://www.pogowasright.org/article.php?story=2008050110324086

Ca: Appearance before the Standing Committee on Access to Information, Privacy and Ethics on Privacy Act Reform

Thursday, May 01 2008 @ 10:32 AM EDT Contributed by: PrivacyNews News Section: Non-U.S. News

Source - Office of the Privacy Commissioner of Canada


It's simple to redefine the world to achieve a single objective. Limiting that change to a single objective is where the problem lies... Watch me make this New York business subject to Colorado sales tax. Click here: http://www.carnegiedeli.com/

http://news.slashdot.org/article.pl?sid=08/05/02/0239248&from=rss

Amazon Fights Back Against NY Online Sales Tax

Posted by Soulskill on Friday May 02, @05:11AM from the fighting-the-good-enough-fight dept.

The New York Times is reporting on Amazon's lawsuit contesting the recently enacted New York state law which requires online retail outlets to collect sales tax on items sold to the state's residents. Amazon disagrees that it should be required to collect such tax without a physical presence in the state. We discussed the 'Amazon Tax' last month. Quoting:

"The new law is based on a novel definition of what constitutes a presence in the state: It includes any Web site based in the state that earns a referral fee for sending customers to an online retailer. Amazon has hundreds of thousands of affiliates--from big publishers to tiny blogs--that feature links to its products. It says thousands of those have given an address in New York State, although it does not verify the addresses. The state law says that if even one of those affiliates is in New York, Amazon must collect sales tax on everything sold in the state, even if it is not sold through the affiliate."


Strategy is as strategy does... (Get all you can before your RICO conviction shuts you down?)

http://yro.slashdot.org/article.pl?sid=08/05/02/0350227&from=rss

Massive Increase in RIAA Copyright Notices

Posted by Soulskill on Friday May 02, @08:18AM from the harnessing-the-power-of-spam dept.

According to Wired, universities in the US are experiencing a "20-fold increase" in the number of takedown notices from the RIAA in the last ten days. Indiana University reports 80 notices a day, but they say their traffic hasn't increased significantly over the same time period. It will be interesting to see if the affected schools join the legal battle against the RIAA, or cave under the increased pressure.

"University of California at Berkeley's chief information officer Shel Waggener confirmed he'd heard of the spikes and suggested there was a political purpose driving them. 'Public universities are in a unique position since the industry puts pressure on us through state legislatures to try to impose what are widely considered to be draconian content monitoring measures and turn us into tech police forces in support of a specific industry,' Waggener said. The RIAA is also backing legislation in states such as Illinois and Tennessee that would require schools that get a certain number of notices to begin installing deep packet monitoring equipment on their internet and intranets, according to Luker."


Another delusional world?

http://yro.slashdot.org/article.pl?sid=08/05/02/1259231&from=rss

SCO's McBride Testifies "Linux Is a copy of UNIX"

Posted by kdawson on Friday May 02, @09:39AM from the can-you-spell-perjury dept. Caldera The Courts Linux

eldavojohn writes

"Here's a short update on the Novell Vs. SCO case we've been following. Our good friend Darl McBride made some interesting comments in court yesterday. He stated (under oath): 'Many Linux contributors were originally UNIX developers... We have evidence System V is in Linux... When you go to the bookstore and look in the UNIX section, there's books on "How to Program UNIX" but when you go to the Linux section and look for "How to Program Linux" you're not gonna find it, because it doesn't exist. Linux is a copy of UNIX, there is no difference [between them]." This flies directly in the face of what SCO found in extensive investigations in 2002 and contradicts what SCO Senior Vice President Chris Sontag had just finished testifying earlier that day (testimony that McBride did not hear)."


Looks like we are trying to match the UK's “a camera in every pot” strategy...

http://www.pogowasright.org/article.php?story=20080502062810450

D.C. Forging Surveillance Network

Friday, May 02 2008 @ 06:28 AM EDT Contributed by: PrivacyNews News Section: Surveillance

The D.C. government is launching a system today that would tie together thousands of city-owned video cameras, but authorities don't yet have the money to complete the high-tech network or privacy rules in place to guide it.

The system will feature round-the-clock monitoring of the closed-circuit video systems run by nine city agencies. In the first phase, about 4,500 cameras trained on schools, public housing, traffic and government buildings will feed into a central office at the D.C. Homeland Security and Emergency Management Agency. Hundreds more will be added this year.

Source - Washington Post


“Gee, if we actually saved and looked at the logs, we might have to do something!”

http://www.pogowasright.org/article.php?story=2008050110280640

Audit: NJ lacks computer security for personal Medicaid data

Thursday, May 01 2008 @ 10:28 AM EDT Contributed by: PrivacyNews News Section: State/Local Govt.

New Jersey has not monitored access to key personal information in a computer system that tracks care for the poor, leaving no way to know if Social Security numbers and other information about doctors and patients have been misused, a recent state audit found.

The analysis determined that the state Department of Human Services lacks appropriate security policies and procedures for the computer system it uses to process claims for more than 1 million New Jersey Medicaid patients.

The department, according to the analysis, fails to properly monitor access to information such as Social Security and tax identification numbers, Drug Enforcement Agency numbers used to write drug prescriptions, and birth dates.

Source - Newsday


Note: This does not address TSA doing similar “searches” domestically...

http://www.pogowasright.org/article.php?story=20080501135225848

Protecting Yourself From Suspicionless Searches While Traveling (updated)

Thursday, May 01 2008 @ 01:52 PM EDT Contributed by: PrivacyNews News Section: Surveillance

The Ninth Circuit's recent ruling (pdf) in United States v. Arnold allows border patrol agents to search your laptop or other digital device without limitation when you are entering the country. EFF and many civil liberties, travelers’ rights, immigration advocacy and professional organizations are concerned that unfettered laptop searches endanger trade secrets, attorney-client communications, and other private information. These groups have signed a letter asking Congress to hold hearings to find out what protocol, if any, Customs and Border Protection (CBP) follows in searching digital devices and copying, storing and using travelers’ data. The letter also asks Congress to pass legislation protecting travelers’ laptops and smart phones from unlimited government scrutiny.

In the meantime, how can international travelers protect themselves at the U.S. border, short of leaving their laptops and iPhones at home?

Source - EFF

Related - The Register: Your personal data just got permanently cached at the US border


For my Computer Security students

http://www.infoworld.com/article/08/05/01/7-dirty-secrets-of-the-security-industry_1.html?source=rss&url=http://www.infoworld.com/article/08/05/01/7-dirty-secrets-of-the-security-industry_1.html

7 dirty secrets of the security industry

At the Interop conference, Joshua Corman, principal security strategist for IBM/ISS, discussed the misconceptions and half-truths surrounding the security industry

By Tim Greene, Network World May 01, 2008

... "The goal of the security vendor is not to secure, it's to make money," Corman says.

He says that is his "zeroth" dirty secret of the security industry. These are the other seven:

1. Antivirus certifications are misleading.

2. There is no perimeter.

3. Risk analysis threatens vendors.

4. There is more to risk than just weak software.

5. Compliance threatens security.

6. Vendor blind spots allowed the Storm worm outbreak to happen.

7. Security has grown well past do-it-yourself.


Another perspective.

http://money.cnn.com/2008/05/01/news/international/usgas_price/?postversion=2008050109

U.S. gas: So cheap it hurts

Relatively low taxes have kept pump prices far below most other developed nations, which some say is precisely why the current runup is so painful.

By Steve Hargreaves, CNNMoney.com staff writer Last Updated: May 1, 2008: 12:18 PM EDT

Most expensive places to buy gas

Rank Country Price/gal

1. Sierra Leone $18.42

2. Aruba $12.03

3. Bosnia-Herzegovina $10.86

4. Eritrea $9.58

5. Norway $8.73

6. United Kingdom $8.38

7. Netherlands $8.37

8. Monaco $8.31

9. Iceland $8.28

10. Belgium $8.22

111. United States $3.45


This is curious. I'll have to give some thought to new venture capital opportunities...

http://hbswk.hbs.edu/item/5928.html

What is the Future of State Capitalism?

Published: May 2, 2008 Author: Jim Heskett Forum open for comment until May 29

Executive Summary:

Whatever happened to the fears not long ago that global corporations with allegiance to no government would challenge the world economic order? These days, state-owned corporations now dwarf even the largest privately-owned global organizations, says HBS professor Jim Heskett. What is impact on competition? What do you think?


If you haven't downloaded and installed the new Ubuntu (8.04) I recommend that you do. Having a dual-boot option lets me play more often with Linux. This is for those of you who tried it.

http://www.killerstartups.com/Web-App-Tools/Medibuntuorg---Free-Ubuntu-Software/

Medibuntu.org - Free Ubuntu Software

Medibuntu, which stands for “Multimedia, Entertainment & Distractions In Ubuntu,” is a packaging product that distributes software that can’t be included in the regular Ubuntu package. Ubuntu is an open source operating system built around Linux, and is generally designed to be something that can be distributed in any country. Because freedom of speech, patent, copyright, license, or other laws vary in different countries, these laws can often preclude the inclusion of a certain software in the Ubuntu package. Medibuntu.com provides packages of software that was not included in Ubuntu for these types of reasons, and distributes them with professional quality packaging that integrates easily with Ubuntu.

http://www.medibuntu.org/